
Recent analysis has uncovered updated tactics, techniques, and procedures (TTPs) used by the Warlock ransomware group (tracked as Water Manaul). While their initial access strategy remains largely unchanged—primarily exploiting vulnerable Microsoft SharePoint servers—the group has significantly evolved its post-compromise operations.
These improvements focus on:
- Stronger persistence mechanisms
- More flexible lateral movement
- Advanced evasion of security controls
New behaviors include:
- Deployment of TightVNC for long-term remote access
- Use of additional open-source tools for command-and-control (C2)
- Continued use of Bring Your Own Vulnerable Driver (BYOVD), now leveraging the NSecKrnl.sys driver
Victim data observed between June–December 2025 shows consistent targeting of:
- Industries: Technology, Manufacturing, Government, Education
- Regions: United States, Germany, Russia, United Kingdom
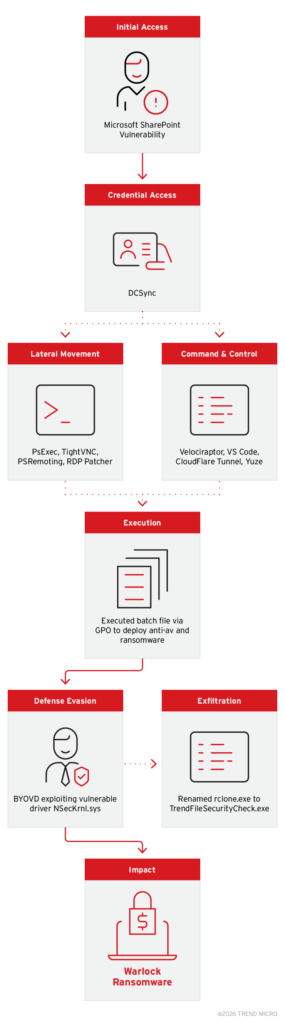
1. Threat Evolution Overview
Although the group still gains entry through unpatched internet-facing SharePoint systems, their toolkit after compromise has grown significantly.
Previously Observed Tools
- Velociraptor (primary C2 framework)
- Cloudflare Tunnel (remote access)
- Rclone (data exfiltration, disguised binaries)
New Additions
- TightVNC
- Installed silently via PsExec
- Runs as a Windows service for persistent GUI access
- Yuze (SOCKS5 proxy tool)
- Lightweight reverse proxy
- Operates over ports 80, 443, and 53
- Updated BYOVD Technique
- Exploits vulnerability in NSecKrnl.sys
- Replaces previously used vulnerable drivers
- Enables kernel-level termination of security tools
These enhancements allow the attackers to maintain multiple redundant C2 channels, blending malicious traffic with legitimate network activity.
2. Attack Lifecycle Analysis
2.1 Initial Access
The attackers continue to exploit Microsoft SharePoint vulnerabilities to gain entry. Activity is often timed during holiday periods, when monitoring is weaker.
- Malicious activity originates from w3wp.exe (SharePoint worker process)
- Execution of Cobalt Strike beacon via DLL sideloading
- Malicious DLL embedded within a seemingly legitimate binary
Key behaviors:
- Communication with external C2 domain
- Obfuscated traffic hidden inside normal web scripts (e.g., jQuery)
- Deployment of process-killing tools to disable defenses
A secondary payload (Velociraptor) is later downloaded from cloud storage (Supabase), indicating use of trusted platforms to avoid detection.
Persistence is established through:
- Batch scripts
- Web shell deployment (
cproxy.aspx) within SharePoint environment
2.2 Credential Access
Attackers perform credential harvesting using:
- Windows Credential Manager access (
rundll32.exe keymgr.dll) - Registry hive dumping
- Mimikatz (historically observed)
DCSync Attack
A tool mimics a Domain Controller to extract credentials via MS-DRSR protocol, allowing full credential replication from Active Directory.
2.3 Lateral Movement
After gaining credentials, the attackers expand access across the network.
Key activities:
- Resetting Administrator account passwords
- Adding users to Domain Admins group
- Full domain compromise achieved
Techniques Used
- PsExec for remote command execution
- PowerShell Remoting (PSRemoting)
- RDP Wrapper/Patcher (enables multiple concurrent sessions)
TightVNC Deployment
Installed via MSI remotely to maintain persistent remote desktop access.
3. Command and Control (C2) Infrastructure
Warlock uses multiple overlapping communication channels for resilience.
Primary Tools
- Velociraptor (abused DFIR tool)
- VS Code tunnels
- Cloudflare Tunnel
Advanced Techniques
- Fileless payload execution using:
[Reflection.Assembly]::Load()- In-memory execution (no disk artifacts)
- Payloads retrieved from public hosting services (e.g., catbox)
Yuze Proxy Usage
- Reverse SOCKS5 tunnels over:
- HTTP (80)
- HTTPS (443)
- DNS (53)
This indicates attempts to bypass firewall restrictions by using commonly allowed ports.
Infrastructure Insight
- C2 IP linked to VPS provider
- Shared infrastructure observed among multiple ransomware groups
4. Defense Evasion (BYOVD Technique)
Warlock continues to disable endpoint protections using vulnerable drivers.
Execution Flow
- Install vulnerable driver (NSecKrnl.sys)
- Use loader (disguised binary)
- Terminate security processes at kernel level
Targets Include
- Endpoint protection platforms (multiple vendors)
- Detection and monitoring services
This method bypasses:
- User-mode protections
- Standard process termination restrictions
5. Data Exfiltration
Data theft is performed using a renamed version of Rclone:
- Disguised as a legitimate executable
- Transfers data to attacker-controlled S3 storage
- Filters specific file types (documents, CAD files, etc.)
This approach blends with normal administrative or backup traffic, making detection harder.
6. Impact: Ransomware Deployment
The final stage involves enterprise-wide ransomware deployment via Group Policy (GPO).
Deployment Method
- Payloads stored in:
SYSVOLNETLOGON
- Automatically distributed to all domain systems
Execution Techniques
rundll32.exeexecuting malicious DLL (RunCryptor)- Backup execution via standalone EXE
Outcome
- File encryption across the environment
- Ransom note dropped (
lockdatareadme.txt)
7. MITRE ATT&CK Mapping (Summary)
| Tactic | Technique |
|---|---|
| Initial Access | Exploit Public-Facing Application (T1190) |
| Execution | PowerShell (T1059.001) |
| Persistence | Web Shell (T1505.003) |
| Privilege Escalation | Exploitation (T1068) |
| Defense Evasion | Rundll32 Proxy Execution, Obfuscation |
| Credential Access | DCSync (T1003.006) |
| Lateral Movement | SMB, RDP, WinRM |
| C2 | Protocol Tunneling, Tool Transfer |
| Exfiltration | Alternative Protocol |
| Impact | Data Encryption (T1486) |
8. Security Recommendations
8.1 Defending Against BYOVD
- Enforce driver allowlisting policies
- Monitor kernel-level driver activity
- Keep all security software fully updated
8.2 Limiting Tool Abuse & Lateral Movement
- Apply application allowlisting
- Restrict tools like PsExec to authorized users only
- Segment administrative networks
- Enforce least privilege access
8.3 Securing External Assets
- Patch all SharePoint servers immediately
- Remove direct internet exposure of RDP/services
- Enforce multi-factor authentication (MFA)
8.4 Improving Detection & Response
- Monitor unusual outbound traffic and tunneling behavior
- Detect abnormal use of developer tools (VS Code, tunnels)
- Maintain immutable, offline backups
- Conduct proactive threat hunting
Conclusion
The Warlock ransomware group is clearly investing in operational maturity, shifting toward:
- Multi-layered persistence
- Redundant communication channels
- Advanced evasion at kernel level
Their continued use of legitimate tools and trusted platforms makes detection increasingly difficult. Organizations must adopt defense-in-depth strategies, combining endpoint hardening, network monitoring, and strong identity controls to reduce risk.
